Global financial networks have officially reached an operational reckoning as post-quantum cryptography banking standards move from theoretical white papers into production clearing houses. With the formalization of NIST quantum-resistant algorithms and escalating warnings surrounding harvest-now-decrypt-later data espionage, major central banks and commercial consortia are overhauling the asymmetric encryption backbones that protect multi-trillion-dollar daily settlement flows. As institutions swap out legacy public-key infrastructure for quantum-resilient lattice schemes, the migration touches everything from real-time gross settlement systems to edge-based hardware security modules.
The Quantum Threat Model Behind Global Financial Infrastructure
Dismantling Asymmetric Encryption Assumptions
For over four decades, wholesale clearing and retail digital banking have relied almost exclusively on discrete logarithm and integer factorization schemes, predominantly RSA-2048, Diffie-Hellman, and Elliptic Curve Cryptography (ECC). Shor’s algorithm proved mathematically that a fault-tolerant quantum computer running sufficient stable logical qubits can resolve these problems in polynomial time. Financial institutions are not waiting for the arrival of a cryptographically relevant quantum machine because cryptographic transitions across legacy cores require seven to ten years of staged infrastructure replacement.
The Real Danger of Store Now, Decrypt Later Exploits
Hostile state actors and coordinated syndicates are systematically intercepting and exfiltrating encrypted interbank payment telemetry, sovereign bond transaction ledgers, and SWIFT payload packets. These intercepted ciphertext payloads sit in massive physical storage arrays waiting for sufficiently powerful quantum compute to break them retroactively. A 30-year sovereign debt instrument or confidential corporate acquisition financing completed today carries obligations spanning decades; exposing the encrypted transaction records ten years down the line yields profound regulatory, legal, and operational exposure.
Why Classical Symmetric Keys Cannot Solve Core Banking Rails
While symmetric encryption like AES-256 remains resilient against Grover’s algorithm by doubling key lengths, symmetric architectures fail completely in distributed transactional ecosystems. Establishing shared secrets across thousands of decentralized correspondent banks without asymmetric key encapsulation mechanisms (KEM) is mathematically and architecturally impossible. Financial hubs cannot operate without scalable public-key cryptography to verify message authenticity, negotiate transport-layer security (TLS) handshakes, and sign non-repudiation receipts across cross-border settlement rails.
Blueprint of the 2026 Bank Consortium Deployments
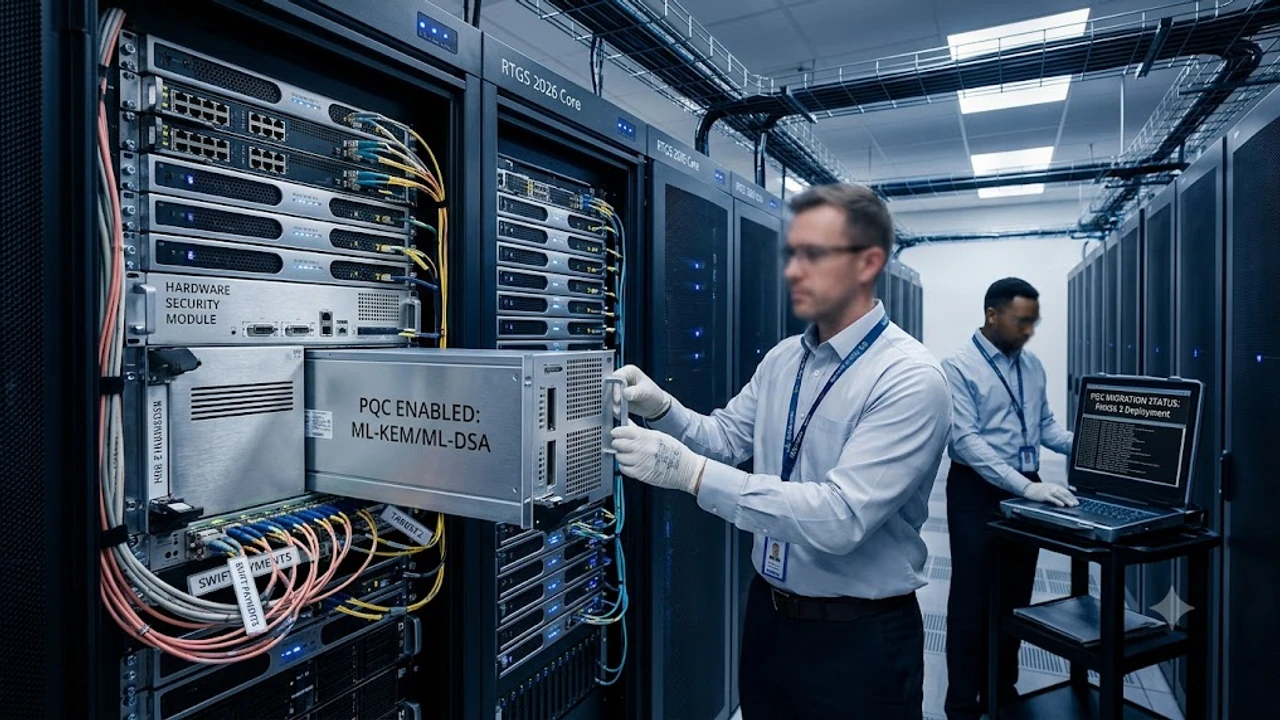
NIST Final Standard Implementations: ML-KEM and ML-DSA
Following the definitive release of Federal Information Processing Standards (FIPS 203 for ML-KEM, FIPS 204 for ML-DSA, and FIPS 205 for SLH-DSA), clearing consortia have abandoned experimental drafts in favor of standardized module lattice primitives. ML-KEM provides the high-throughput key encapsulation required for ephemeral TLS sessions between core ledger APIs, while ML-DSA handles digital signatures for interbank batch authentication. These algorithms trade computational efficiency for significantly expanded key footprints, forcing network engineers to re-evaluate MTU sizes and packet fragmentation across cross-border transit backbones.
Hybrid Cryptographic Implementations on Live Payment Rails
Rather than executing abrupt hard forks on payment switches, engineering teams at institutions like JPMorgan Chase, Deutsche Bank, and BNP Paribas are deploying dual-layer hybrid schemes. An inbound payment instruction must pass both a classical ECDSA verification check and an ML-DSA verification check in parallel. If either layer fails, the transaction is isolated to an anomaly queue:
“Dual-signature hybrid architectures provide algorithmic fault isolation: should a structural mathematical weakness emerge in post-quantum lattice proofs, classical security envelopes prevent unauthorized state execution, and vice versa.”
This transitional approach mirrors earlier architectural shifts where secure local intelligence had to integrate alongside broader networks, a concept examined in Why IFA 2026 Shifted to On-Device AI: 3 Key Takeaways. By running concurrent cryptographic pipelines, clearing nodes ensure continuity without exposing raw core accounts to unverified code paths.
High-Throughput Hardware Security Module Modernization
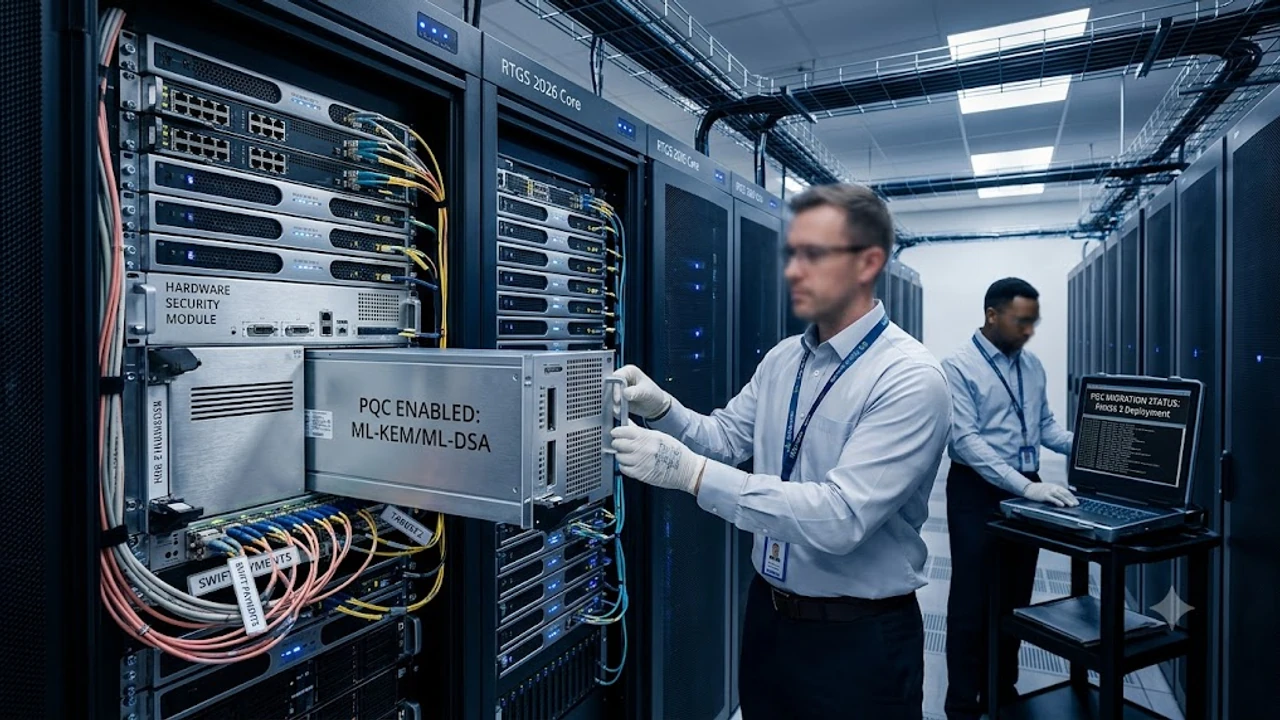
At the physical data center tier, legacy Hardware Security Modules (HSMs) are hitting structural memory barriers. Traditional PCI-e cryptographic cards were engineered around 256-bit to 2048-bit key buffers, while post-quantum ciphertexts and public keys measure thousands of bytes. Tier-1 financial institutions are aggressively swapping legacy appliance clusters for crypto-agile HSM platforms featuring specialized application-specific accelerators designed to calculate high-dimensional polynomial matrix arithmetic without introducing catastrophic latency spikes into high-frequency trading matching engines.
Global Regulatory Mandates and Cross-Border Interoperability
Federal Reserve and European Central Bank Directives
Both the Federal Reserve Board and the European Central Bank (ECB) have published stringent transition timelines requiring critical financial market utilities (FMUs) to produce exhaustive cryptographic bills of materials (CBOMs). Regulatory compliance examinations now audit every endpoint, middleware broker, and microservice to map hidden cryptographic dependencies. Regulators have stated that institutions unable to show verified quantum-safe ingress endpoints for wholesale payment settlements by the close of fiscal 2026 face capital charge surcharges under operational resilience risk frameworks.
The Korean Financial Services Commission Action Roadmap
In Asia, the South Korean Financial Services Commission (FSC) and Financial Supervisory Service (FSS) established a fast-track quantum migration compliance task force for the domestic banking sector. Working alongside major telecommunications infrastructure providers and national research centers, South Korea’s commercial powerhouses—including Shinhan, KB Kookmin, and Hana Bank—have initiated pilot programs combining post-quantum mathematical algorithms with quantum key distribution (QKD) fiber trunks across metropolitan financial zones in Seoul. Korean regulators have emphasized securing the public key certificates underpinning nationwide retail banking and cross-border trade settlements against foreign surveillance.
Cross-Border SWIFT Messaging Upgrades and ISO 20022 Alignment
The primary friction point in global post-quantum deployment centers on message syntax overhead. Standard ISO 20022 XML payment formats must carry significantly bulkier digital signature envelopes. SWIFT has orchestrated pilot corridors between Frankfurt, New York, and Tokyo to stress-test upgraded parsing engines, ensuring that multi-kilobyte signatures do not trigger buffer overflow exceptions or cross-border payment timeouts during peak trading windows.
Strategic Playbook for Financial Institutions and Edge Nodes
Continuous Discovery and Cryptographic Inventory Auditing
Chief Information Security Officers cannot protect assets they cannot locate. Financial enterprises are deploying automated discovery tooling to continuously scan source repositories, container registries, compiled binaries, and network interfaces for hardcoded legacy keys or unmanaged certificates:
- Algorithm Dependency Mapping: Catalog every instance of RSA, DSA, and ECC across both customer-facing applications and back-office mainframes.
- Dependency Graph Analysis: Trace how identity and access management (IAM) frameworks link with session negotiation proxies.
- Vendor Protocol Validation: Demand verified cryptographic roadmaps from third-party enterprise resource planning (ERP) and payment gateway vendors.
Designing for Long-Term Cryptographic Agility
The definitive lesson from the post-quantum pivot is that no mathematical primitive is permanent. Future algorithmic cryptanalysis could expose vulnerabilities in current lattice formulations, requiring further protocol adjustments. Modern financial software architectures are decoupling application logic from cryptographic providers via pluggable abstraction layers. Standardizing on modular security interfaces allows institutions to swap cryptographic primitives in hours rather than executing multi-year code refactoring programs.
Hardware Edge Protection and Physical Token Refresh
Securing the central clearing switch represents only half the challenge; consumer edge authenticators, enterprise physical security tokens, and corporate treasury keys require hardware upgrades. Leading cryptographic manufacturers are introducing next-generation FIPS-certified smart cards and hardware keys equipped with post-quantum signature verification coprocessors, ensuring that end-to-end commercial banking workflows remain unassailable from client browser to central bank vault. To secure enterprise operations and maintain hardware authentication security, explore dedicated enterprise security gear:
#GlobalTrends #PostQuantum #Cybersecurity #Banking #Fintech #Infrastructure #Korea #2026